VULN-X // OWASP SCANNER
Vuln-X — Automated Web Security Assessment
VULN-X
Automated Web Security Assessment
Powered by OWASP Top 10 (2017)

Find vulnerabilities before attackers do.

Scan web applications against OWASP Top 10 security risks with automated detection, evidence collection, and professional security reports — no setup required.

OWASP Top 10 (2017) · Automated Scanning · Security Reports · Vulnerability Detection
[+] Initializing scan engine...
[•] Testing for SQL Injection...
[•] Checking XSS payloads...
[•] Analyzing security headers...
[✓] Scan complete. 2 vulnerabilities found.
Ethical Use Only
"Security is not a product, but a process. It's a way of thinking, not just a set of tools."

— Bruce Schneier, Security Technologist

"Amateurs hack systems. Professionals hack people — and attackers always target the weakest link."

— Kevin Mitnick, World's Most Famous Hacker

"The only truly secure system is one that is powered off, cast in concrete, and sealed in a lead room."

— Gene Spafford, Cybersecurity Professor

"If you know the enemy and know yourself, you need not fear the result of a hundred battles."

— Sun Tzu, The Art of War (Applied to Pentesting)

0
OWASP Categories
<5 min
Avg Scan Time
0
Scan Modules
0
Report Formats

Core Capabilities (OWASP Top 10 2017)

A1 - Injection

Detects SQL injection, NoSQL injection, OS command injection, and other injection flaws where untrusted data is sent to an interpreter.

A2 - Broken Authentication

Identifies session management flaws, weak authentication mechanisms, and credential handling issues that allow account compromise.

A3 - Sensitive Data Exposure

Scans for improper protection of sensitive data, including weak encryption, missing encryption, and exposed credentials.

A4 - XML External Entities (XXE)

Checks for XXE vulnerabilities where XML parsers process external entity references unsafely, leading to data exposure.

A5 - Broken Access Control

Finds issues where users can act outside their intended permissions, accessing unauthorized data or performing restricted actions.

A6 - Security Misconfiguration

Detects insecure default configurations, missing security hardening, unnecessary features, and improper error handling.

A7 - Cross-Site Scripting (XSS)

Identifies reflected, stored, and DOM-based XSS vulnerabilities where malicious scripts are injected into web pages.

A8 - Insecure Deserialization

Scans for deserialization flaws where untrusted data is processed, potentially leading to remote code execution attacks.

A9 - Vulnerable Components

Checks for outdated libraries, frameworks, and components with known vulnerabilities that could be exploited.

A10 - Insufficient Logging

Evaluates logging and monitoring gaps that could allow attacks to go undetected, hindering incident response and forensics.

Get Your Report in 3 Simple Steps

1Enter Your Target

Add a website address or IP on the New Scan page — a domain or full URL works best, and the scanner resolves the rest.

2Choose Your Scan

Pick one or more OWASP Top 10 categories — Injection, XSS, Broken Access Control and more — or run a Full Scan across all 11 modules.

3Get Your Report

Review findings instantly with severity breakdowns and evidence, then download a professional PDF or export the raw JSON.

Professional UI. Clear Results.

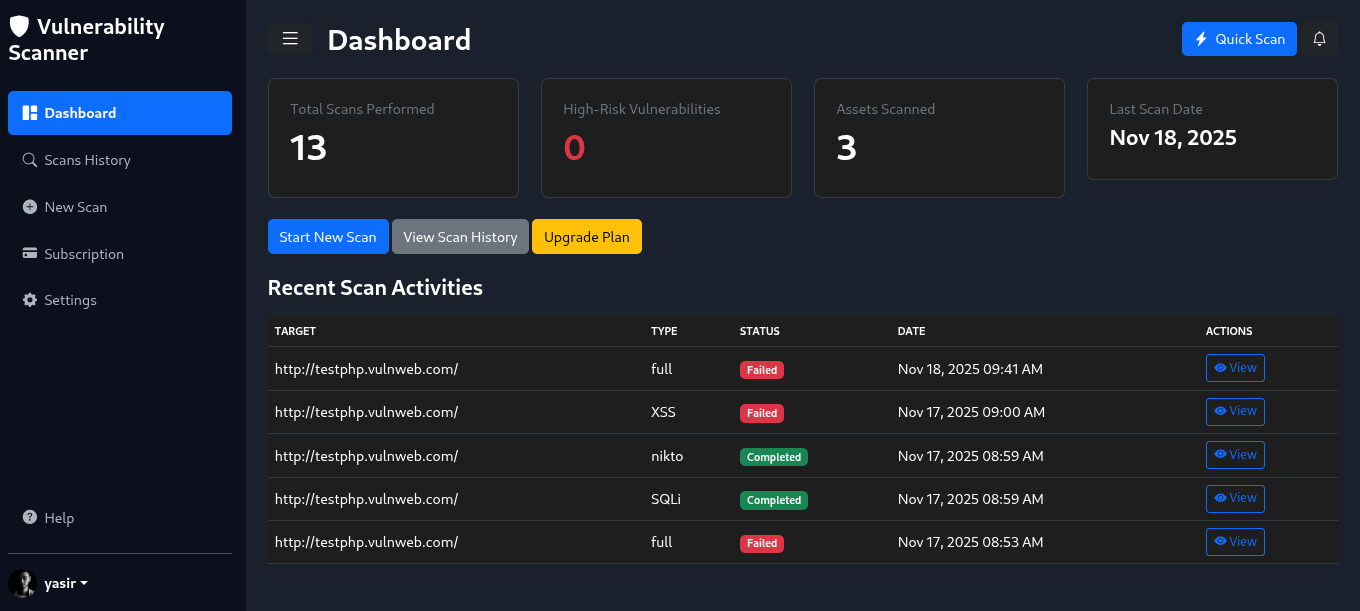
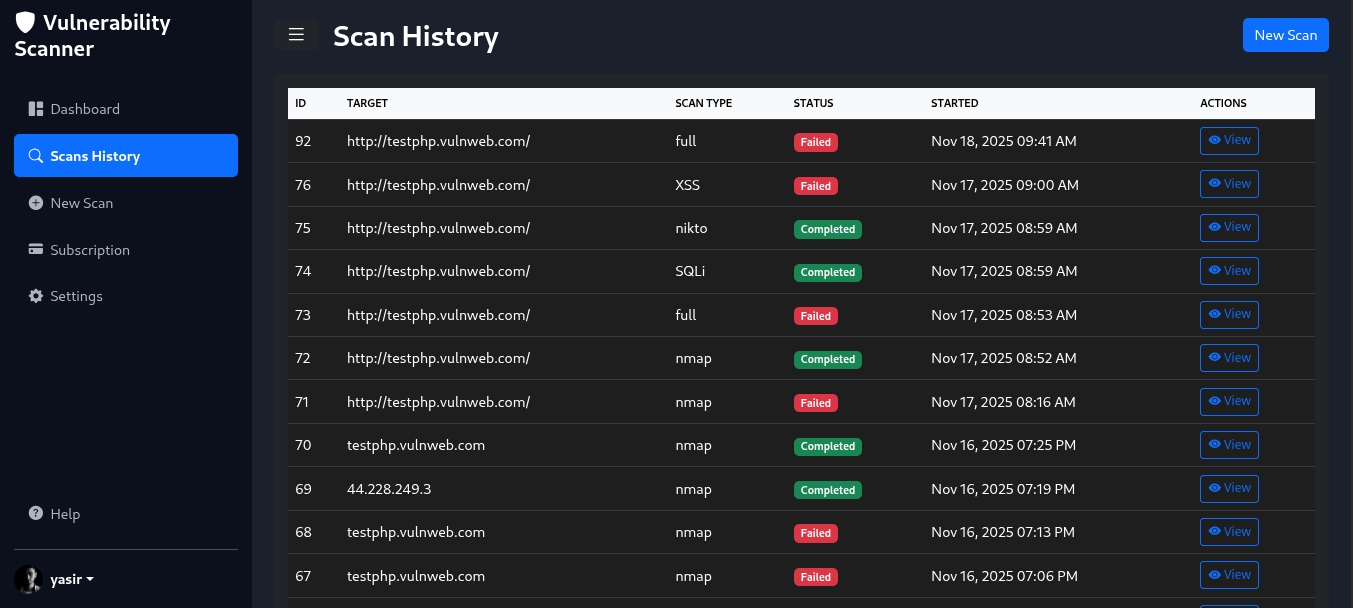
Our powerful dashboard is designed to be intuitive for beginners yet feature-rich for security professionals. View your findings, track history, and generate comprehensive reports seamlessly.

$ vuln-x scan https://example.com
[+] Target: example.com
[!] SQL Injection detected on /login endpoint
[!] Missing Security Headers: X-Frame-Options, CSP
[✓] XSS: Not Found
[✓] CSRF: Not Found
$ Scan complete — 2 vulnerabilities found
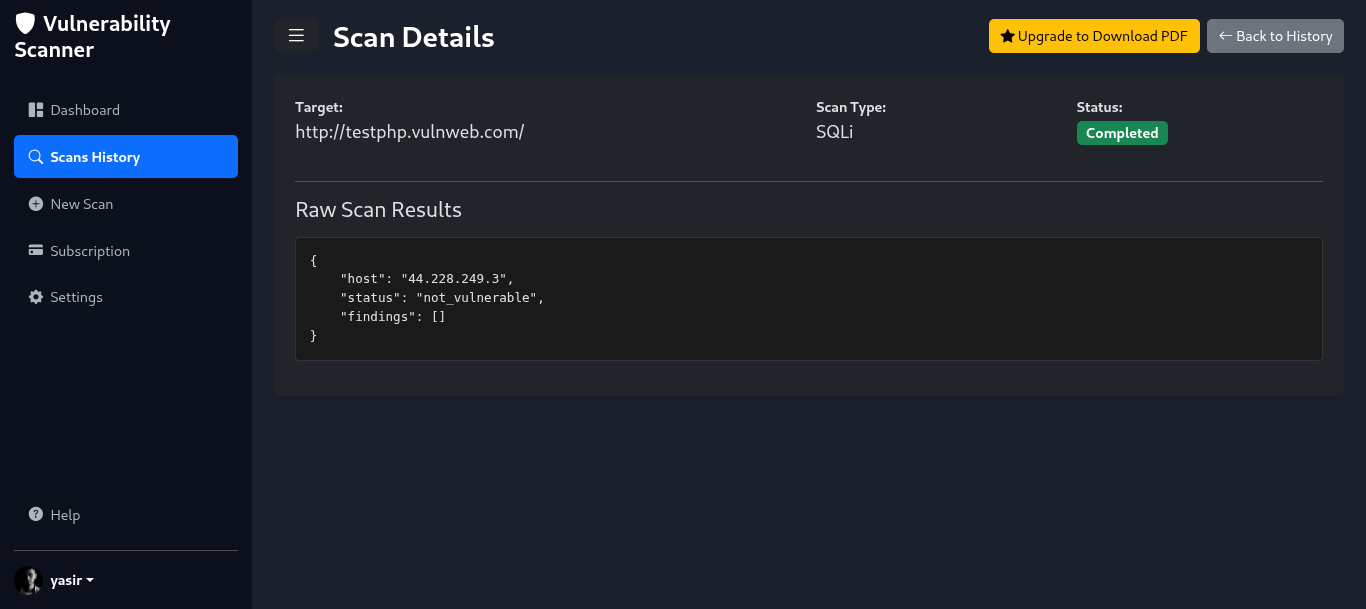
Main Vuln-X Dashboard Screenshot
Scan History and Tracking Page Screenshot
Automated Scanner PDF Report Preview

Why Choose Our Scanner?

No Installation Needed

Fully web-based. Runs directly in your browser with zero setup.

Fast & Automated

One-click scanning with pre-built, professional scanning modules.

Beginner Friendly

Designed for users with zero cybersecurity experience. No coding needed.

Professional Reports

PDF + JSON + Charts included for every premium scan.

Safe & Ethical

Scans are only allowed on authorized websites. We enforce ethical use.

Free Plan Available

Get one free scan to test the platform before you decide to upgrade.

Find the Plan That Fits Your Security Needs

Choose a plan to unlock professional vulnerability scanning capabilities.

Starter Plan

Perfect for students & beginners.

₨900/month

3 scans / subscription month

  • Basic Vulnerability Scanning
  • All 10 OWASP Categories
  • Full Scan History
  • Full Scan Mode
  • Basic Analytics
  • PDF Reports
Choose Starter

Enterprise Plan

Ideal for organizations.

₨30,000 Save ₨3,000
₨27,000/year

120 scans / subscription year

  • 120 Scans / Year
  • Full OWASP Scan Mode
  • Real-Time Scan Monitoring
  • Advanced Analytics Dashboard
  • Team Accounts (5 users)
  • Priority Processing & Support
Choose Enterprise

We support manual payments via Easypaisa, JazzCash, Nayapay, and Sadapay. View Payment Details

Who Is This For?

"This was the perfect tool for my Final Year Project. I could test my web app for vulnerabilities and learn hands-on."

Students
Learn web security hands-on.

"A simple, one-click tool to run basic security checks on my own apps before deployment. Saves me time."

Developers
Test your own apps easily.

"Our team uses this to get quick results on non-critical assets, reducing manual work and saving us time."

Small Businesses
Reduce manual work and save time.

Frequently Asked Questions

Everything you need to know about Vuln-X and OWASP-based scanning.

The OWASP Top 10 is the industry-standard awareness document for web application security, representing the most critical security risks. Vuln-X is built around the 2017 edition and automatically tests your applications against all 10 categories — from Injection attacks to Insufficient Logging & Monitoring.

No. You may only scan websites that you own or have explicit written permission to test. Scanning unauthorized targets is illegal and will result in immediate account suspension. Vuln-X is designed for ethical security testing only.

Vuln-X tests all 10 OWASP Top 10 (2017) categories — Injection, Broken Authentication, Sensitive Data Exposure, XXE, Broken Access Control, Security Misconfiguration, XSS, Insecure Deserialization, Vulnerable Components, and Insufficient Logging & Monitoring — plus a Reconnaissance module (11 modules total). You can run any single category on its own, or a Full Scan that runs them all. Full Scan is available on every paid plan (Starter, Professional, and Enterprise).

The free plan gives you 1 scan to test the platform with basic vulnerability checks. For more scans, PDF reports, and advanced analytics, upgrade to a Starter, Professional, or Enterprise plan.

Currently, Vuln-X supports manual payments via Easypaisa, JazzCash, Nayapay, and Sadapay. After payment, your account is manually upgraded within 24 hours. Visit the Subscription page for full payment instructions.

Absolutely. Vuln-X is designed with beginners in mind. No command-line knowledge or coding experience is required. The dashboard is fully visual with explanations for every vulnerability found — making it an excellent learning tool for students starting their security journey.

Security & Legal Compliance

This tool is for ethical testing only. You may scan only applications you own or have explicit written permission to test. Unauthorized scanning is illegal and will result in an immediate account ban.